Users, teams and roles
Invite people, change their organization role, suspend or remove them, and use teams to grant access to workspaces.
People join an organization by invitation, and reach workspaces through teams. The rules behind roles and access are in Access model.
Before you start
- Inviting, changing roles, suspending and removing people needs the Owner organization role.
- Creating teams, managing their members and granting them workspace access needs the Owner organization role.
- Every other member reads the same lists without these actions: Invite user, a person's actions, New team, Restrict all workspaces and the bin icons are shown only to whoever may use them. A team's Workspace access, and a person's, list only the workspaces you can view.
Invite people
- Open Settings, then Users, and select Invite user.
- Enter the Email address, First name and Last name.
- Choose a Role: Viewer, Editor or Integration owner. Viewer is preselected, and the dialog describes the role you choose; see what each role can do.
- Select Send invitation. The confirmation offers Add to a team, which opens Teams: the person reaches the workspaces the Everyone team can access, and those of the teams you add them to.
The person is listed as Invited until they accept, and the list shows when the invitation expires. Resend invite sends it again, with a new link valid for seven days; inviting the same address again instead is refused with "An invitation for this address is pending; resend it instead". An organization sends at most 100 invitations in any 24 hours, and at most 3 to one address, resends included; past either, sending is refused until the oldest of them is 24 hours old. Remove on an invited person withdraws the invitation, and its link stops working. The Owner role cannot be given by invitation.
Accept an invitation
The link in the invitation email opens a page that names the organization, the address the invitation was sent to and the role it gives.
- Without a Costfluent account, choose how you will sign in as the invited address: enter a Password and select Accept invitation, or, where the page offers them, use a provider account for that address or select Use a passkey instead.
- With an account already, select Join to join; opening the link alone changes nothing, and Not now leaves the invitation pending. After joining, the button below names the address to sign in as.
- Where the organization requires single sign-on for your address, select Continue with single sign-on: signing in there joins.
A provider account with another address is refused: open the invitation email again and use a password, a passkey or a provider account for the invited address. A link that has expired, was used already or was withdrawn shows Invitation link not valid: ask the person who invited you to send the invitation again, or sign in if you already accepted it. If the page could not reach Costfluent, or too many requests came from your network, the invitation stays unused and the page says so; try again.
Change a role, suspend or remove
Open a person's actions on Settings, then Users:
- Change role sets their organization role. Each choice in the dialog says what the role can do, and What each role can do below them opens the access model. Choosing Owner asks you to confirm. Another Owner can be lowered to another role while at least one other active Owner remains, and while single sign-on is enforced, another break-glass Owner too; the last one keeps the Owner role. The same holds for your own role: on your own row, Change role is the only action, offered while another active Owner remains.
- Suspend takes their access away until Reactivate. You cannot suspend yourself or the organization's last active Owner.
- Sign out ends every session of the person, in every organization they belong to, within 15 minutes; they can sign in again. You sign yourself out on Security instead; see Sign-in and security.
- Remove takes them out of the organization and every team in it. The organization and workspace API tokens they created stop working until they rejoin; service tokens keep working. To bring them back, invite them again; to pause their access instead, suspend them. Another Owner can be removed while another active Owner remains; you cannot remove yourself or the organization's last active Owner; to go yourself, leave the organization.
The Removed tab lists the people who were removed. Their rows offer no actions.
Leave an organization
- Open the account menu at the top right while you are in the organization, and select "Leave" followed by the organization's name.
- Confirm with Leave.
You lose access to the organization and every team in it, and Costfluent opens another organization of yours; with none left, you start by creating one. To come back, an Owner has to invite you again. The organization's last active Owner cannot leave, and while single sign-on is enforced neither can its last break-glass Owner; Costfluent says why. Someone working in an organization for the partner that manages it has no membership there to leave.
Create a team
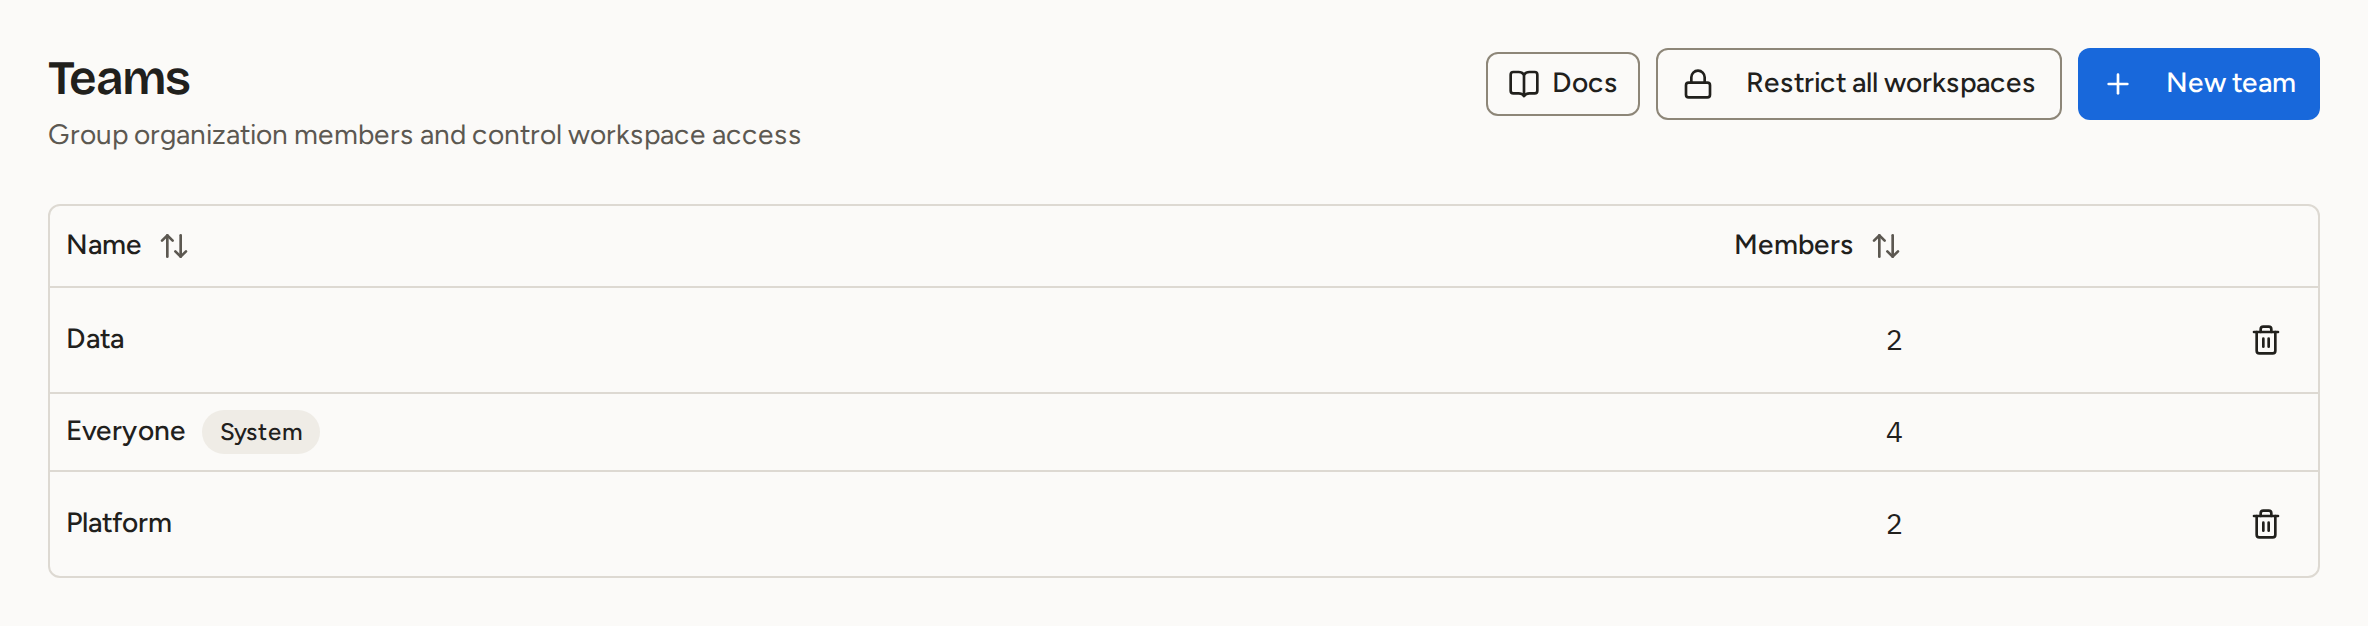
- Open Settings, then Teams, and select New team.
- Enter a Team name and select Create team. The team's page opens, where you add its members and grant it workspace access.
Teams lists each team with its number of Members. Every organization also has the system team Everyone, marked System; see Access model.
Add members
Open the team. Under Members, choose the person and their team role, Viewer or Editor, then select Add member; the card links to how these roles work. Change a member's team role in the list, or remove them from the team; they keep their organization membership and lose only what this team grants. A team role never goes above the person's organization role: a Viewer can only be a team Viewer, and the list says so under their role. Members of Everyone follow their organization role and have no role to change.
Grant workspace access
Under Workspace access on the team, choose the workspace and the level, Can view or Can edit, then select Grant access. Change the level in the list, where No access is offered too, or remove the access.
Every member is also on the Everyone team, so a team's grants limit no one while the Everyone team still reaches a workspace. Until you restrict all workspaces, the card on a team other than Everyone says so, with Open the Everyone team.
Give a team a default dashboard
Under Workspace access on a team, an Owner chooses a Default dashboard for each workspace the team can view or edit: the dashboard of that workspace its members open after signing in or switching to it, unless they chose their own with Set as my default. A member of several teams with one opens the default of the team they joined first. None clears it. The Everyone team and a workspace the team has No access to have none. Changing the team's level keeps its default; removing its access ends it, and deleting the dashboard clears it. A default set with Terraform, on costfluent_team_workspace_access, shows a change made here on its next plan.
Restrict all workspaces
- Open Settings, then Teams, and select Restrict all workspaces.
- Select Restrict to confirm.
Everyone gets No access on every workspace, and workspaces created afterwards start with No access for it, so people reach a workspace only through a team you grant. Restricting again changes nothing.
Check a person's workspace access
On Settings, then Users, select the workspace access icon at the end of a person's row. Every member can open it. It lists each workspace you can view with the access the person reaches there, and every team that grants it with that team's level and the role the person acts with. An Owner reaches every workspace as the organization's owner. Select a team's name to open that team, where its access is changed. If the access cannot be loaded, Retry reads it again.
Delete a team
On Teams, select the bin icon at the end of the team's row, then Delete to confirm. Its members keep their organization membership and lose only what the team granted. The system team Everyone cannot be deleted.