Sign-in and security
Sign in with a password, a passkey, GitHub, Google or Microsoft, manage your passkeys, authenticator app, connected accounts and connected apps, and connect your identity provider over OpenID Connect.
Each person chooses how they sign in. An organization Owner can also connect the company's identity provider for single sign-on; what that does today is set out under Connect single sign-on.
Before you start
- Passkeys, the authenticator app and connected accounts are personal: open the account menu, then Security.
- Single sign-on needs the Owner organization role.
Sign-in methods
The sign-in page asks for your Email address first, then your Password, then a code. On the first step it also offers:
- Sign in with a passkey, in a browser that supports passkeys;
- Sign in with GitHub, Google or Microsoft, where the deployment offers them.
Planned: sign-in with Microsoft
Microsoft signs in work and school accounts whose organization has verified its email domain with Microsoft: such an account signs in to the Costfluent account with that address, or opens one. Microsoft does not vouch for any other address, so any other Microsoft account, personal accounts included, is refused; sign up with a password or another provider instead.
When your company's domain has single sign-on enabled, the sign-in page recognises it from the email address and sends you to your identity provider instead of asking for a password. The sign-up page does so only where the connection creates accounts or single sign-on is required, as Enable and enforce explains. See Connect single sign-on.
After your password, the sign-in page asks for a six-digit code before it signs you in. If you have set up an authenticator app, it asks for the app's code. Otherwise Costfluent emails a code to your address, under the subject "Your sign-in code - Costfluent", or "Ihr Anmeldecode - Costfluent" if your language is Deutsch. The code works once, and expires after 10 minutes or when you ask for a new one; Send a new code sends one at most once a minute. Five wrong codes, emailed or from the app, lock the code step for up to 15 minutes. Signing in with a passkey, a connected account, single sign-on or an email confirmation link never asks for the emailed code. Under Sessions, a session opened with the emailed code reads Password and emailed code. If a code arrives when you did not sign in, someone knows your password: change it, and select Sign out everywhere else under Sessions.
A session renews itself while you use it, and ends after 7 days without use. However recently you used it, it ends 30 days after you sign in, or 24 hours after when it began through single sign-on; then you sign in again. When a session ends while you are away, the sign-in page says why: it ran out, it was idle, you or an Owner signed it out, or the password or email address changed. Group changes at your identity provider therefore apply at that next sign-in, within a day. Where Require single sign-on is on, someone removed at your identity provider cannot sign back in, unless they are a break-glass Owner.
Reset your password
If you forgot your password, select Forgot password? on the sign-in page, enter your Email and select Send reset link. If the address signs in with a password, Costfluent emails it a link to set a new one. The link works once and expires after 1 hour: open it, enter the new password under New password and Confirm password and select Reset password. Every session of the account is then signed out, and you sign in with the new password.
- An account that signs in with GitHub, Google, Microsoft, a passkey or single sign-on has no password, so it gets no email: sign in the way you signed up. To add a password, sign in and select Email me a link to set one under Password in Security.
- Asking again for the same address within one minute sends no second email, so wait for the first. A later request sends a new link, and the earlier one stops working.
- The page answers alike whether or not the address has an account. Only when too many requests come from your network does it say so instead, with how long to wait.
- A link that has expired or was used already offers Request a new link.
When your password is refused
After a wrong password the sign-in page says "Invalid email or password". It says the same for an address without an account, for an account that has no password and while password sign-in is paused, so it reveals nothing about an account; below it, it names the ways out.
- An account made with GitHub, Google, Microsoft or a passkey has no password: select Change and sign in the way you signed up.
- After 10 wrong passwords in a row, signing in with a password pauses for 15 minutes. During the pause every password is refused, the right one too, except in a browser where you set your current password, or where you last signed in recently and with that password: there the right password still signs you in. Costfluent emails the account's address when the pause starts, under the subject "Password sign-in paused - Costfluent", or "Anmeldung mit Passwort ausgesetzt - Costfluent" if your language is Deutsch, with a Reset password button: a new password signs you in at once. A passkey or a connected account still signs you in meanwhile.
- A right password before then starts the count again. A wrong password typed to confirm it is you counts the same.
Add a passkey
- Open Security and, under Passkeys, select Add passkey.
- Keep or change the Device name, which starts as this browser and its system, such as "Chrome on macOS", then select Add passkey and confirm with your fingerprint, face or device PIN.
Each passkey shows when it was added and last used. Rename changes its name, so passkeys on different devices can be told apart; the passkey signs you in as before. Remove stops it working on that device. If it is the only way you can sign in, Remove is refused until you add another passkey or connect a GitHub, Google or Microsoft account. A browser without passkey support says so, and Add passkey stays unavailable there.
Each time a passkey is added here, Costfluent emails your address, in your language, with when it was added. A passkey signs you in on its own, without your password, so if you did not add it, select Remove for it, then Sign out everywhere else under Sessions, and change your password.
Set up an authenticator app
An authenticator app adds a six-digit code to every sign-in, in place of the code Costfluent otherwise emails after your password, and is what an organization that requires two-factor authentication asks for; the emailed code does not meet that requirement.
- Open Security and, under Authenticator app, select Set up.
- Scan the QR code with your authenticator app, or add Costfluent with the Secret key or Open in authenticator app.
- Enter the Authentication code the app shows and select Verify.
- Store the recovery codes shown under Save your recovery codes, with Copy codes or Download, which saves them as a text file, then select Done. They are shown only this once; each signs you in once if you lose the app.
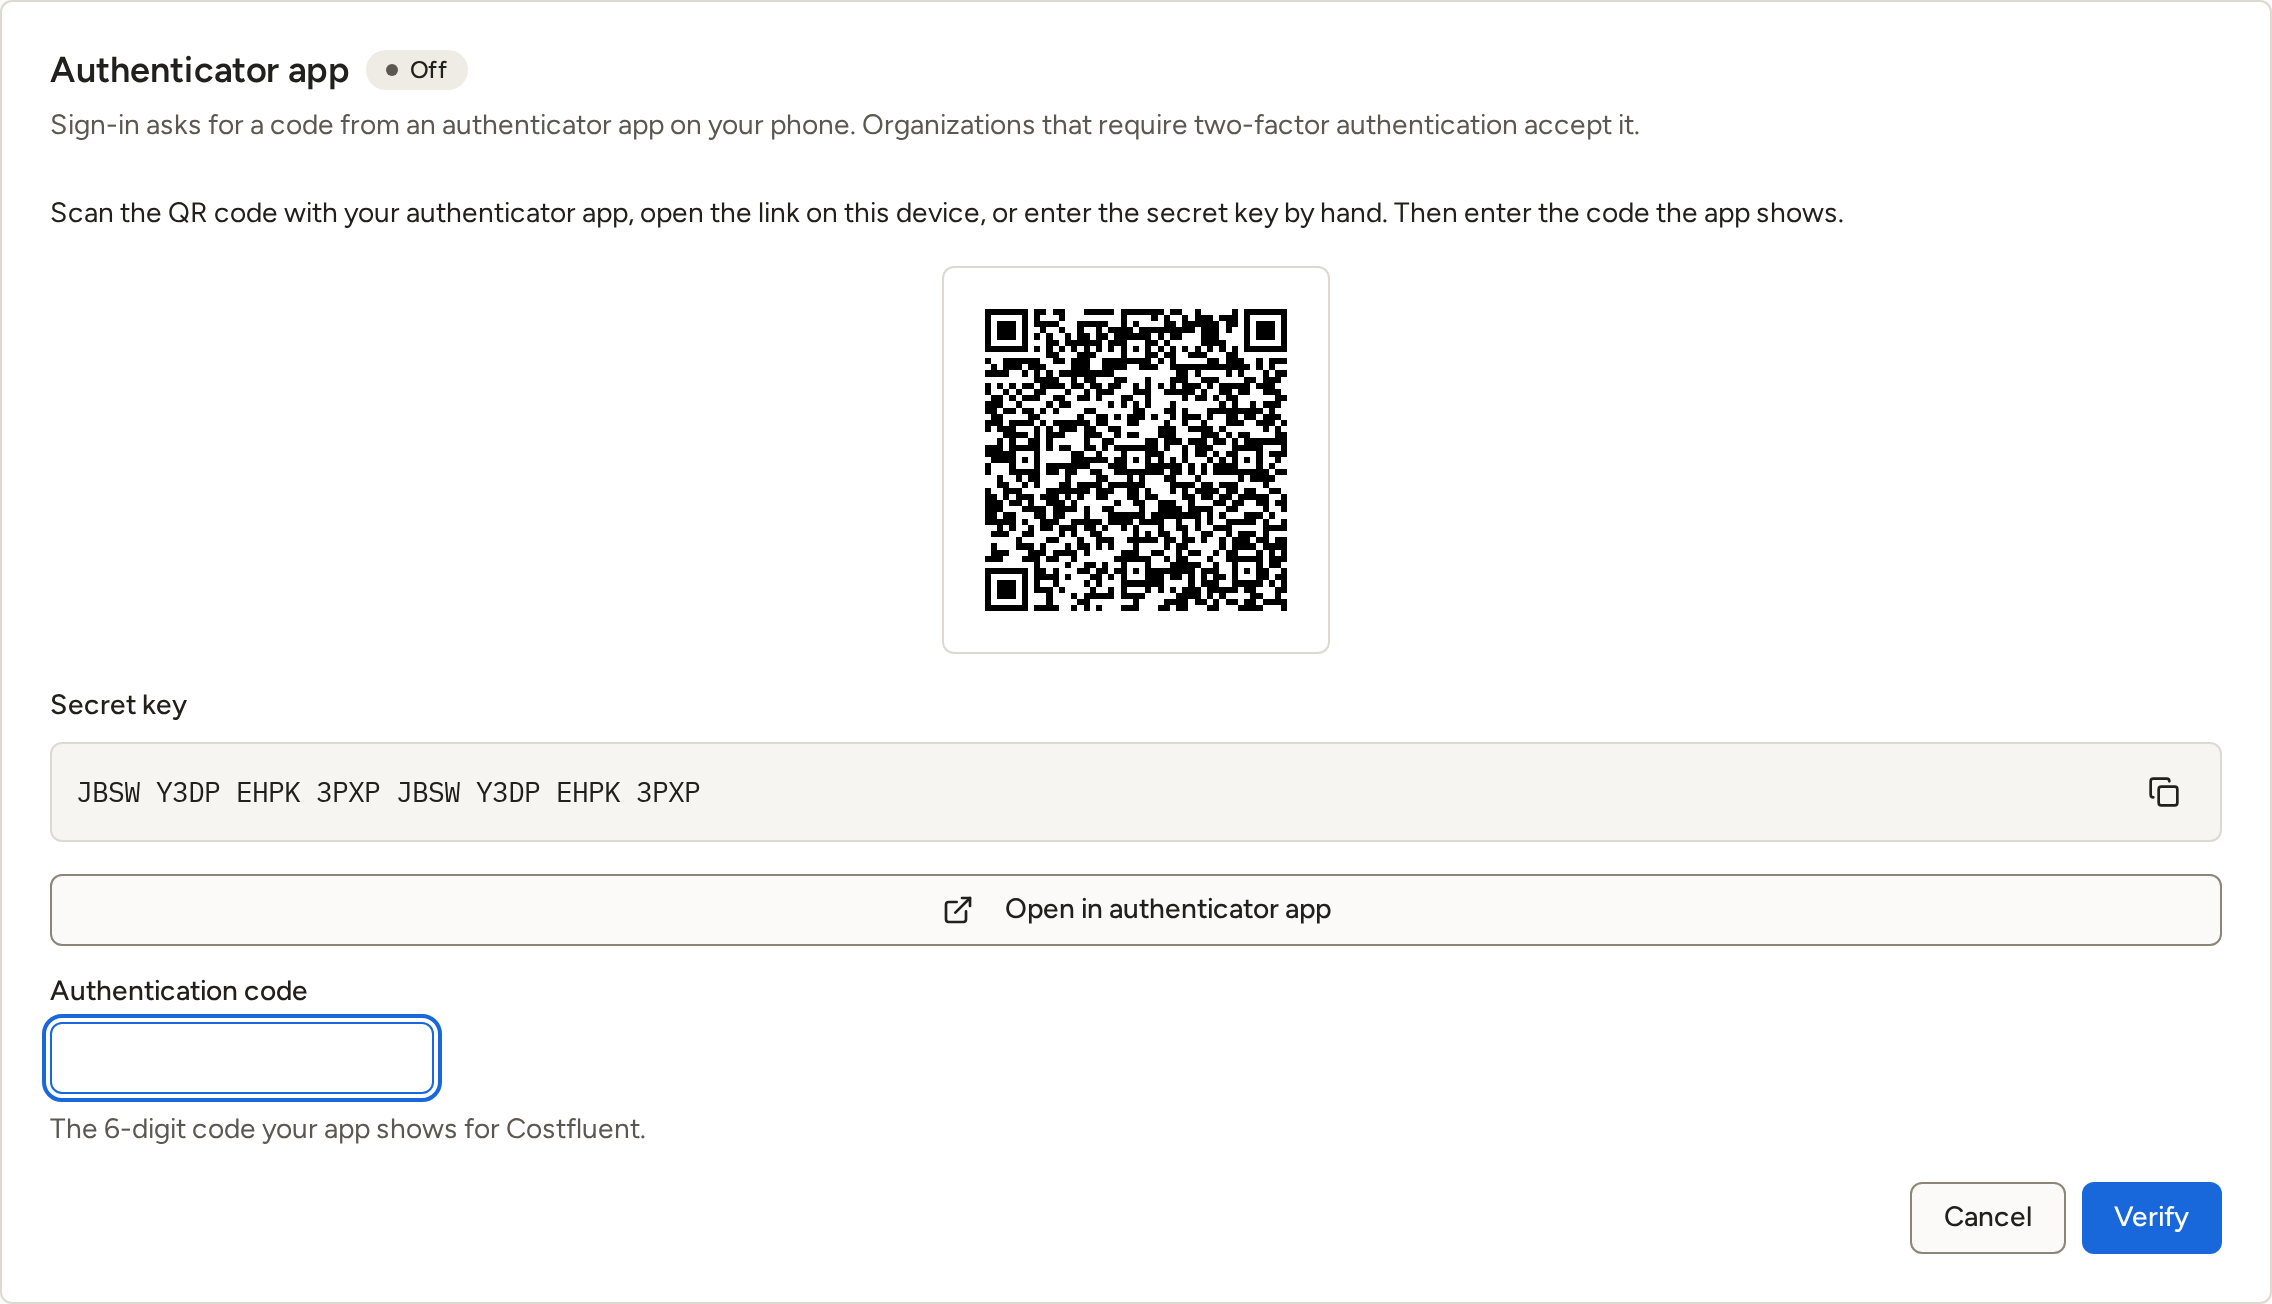
The section shows On or Off. Setting one up needs a recent sign-in. Remove asks for your Current password and a Code or recovery code. An account without a password, made with a passkey or a connected account, gives only the Code or recovery code and needs a sign-in from the last 60 minutes; confirming it is you does not count here. After that, Remove offers Sign in again.
Sessions, password and recovery codes
Security also lists your Sessions: every browser and device signed in to your account, with how and from which address it signed in, when, and when it was last active; this browser is marked This device. Sign out ends one session, and Sign out everywhere else ends all but this one. A device that is signed out stops working within 15 minutes.
Some changes need a recent sign-in: a sign-in, or a confirmation that it is you, from the last 60 minutes. They are the changes that hand out lasting access, change who can get in, send data out of Costfluent or erase it, such as creating an API token, inviting someone or changing their role, changing single sign-on, the two-factor requirement or whether AI agents may create and change objects, adding a cluster, deleting a workspace, a cluster or a connection, and changing the plan or the payment method. Removing someone from a team set to Cannot enter for an organization you manage as a partner, or deleting such a team, asks too, since it can let them into that organization, and so does removing a suspended member who works for the partner that manages your organization. From an older session, Costfluent asks you to confirm it is you, with a passkey that checks it is you (by fingerprint, face or PIN), a code from your authenticator app or your password, and then makes the change where you are, without signing you out or clearing what you entered; Sign in again, which it also offers, leaves the page instead, and what you entered is lost. Your password alone is enough only on an account with no passkey and no authenticator app, while no organization you belong to requires two-factor authentication. A passkey or authenticator app added since you signed in confirms nothing until you sign in again with it. Confirming does not change when you signed in, so the session still ends when it would have. An account that has no way to confirm, such as one that must sign in with single sign-on and is not a break-glass Owner, is asked to sign in again instead.
Under Password, enter your Current password and the New password twice, then select Change password; your other sessions are signed out. An account without a password, made with a passkey or a connected account, can select Email me a link to set one instead. If you have a password but forgot it, select Email me a link under Forgot your current password? for a link that resets it.
While you have an authenticator app, Recovery codes shows how many unused codes are left and warns when few are, or says when none are. Generate new codes asks for your Current password and an Authenticator code, then shows a new set once, with Copy codes and Download; the old codes stop working. An account without a password gives only the Authenticator code and, as for removing the app, needs a sign-in from the last 60 minutes, else it is offered Sign in again.
An Owner can also sign a member out: open Settings, then Users, and select Sign out in the member's actions. That ends every session of the member, in every organization they belong to, since a session belongs to the person rather than to one organization; they can sign in again. Users shows under Second factor whether each member has an authenticator app and how they last signed in.
If you lose your authenticator app
Without the app, sign in with a recovery code: after your password, enter one under Authentication code, where the app's code would go. Each recovery code works once. Then open Security, select Remove under Authenticator app, confirm with another recovery code under Code or recovery code, and set up the app again on your new device, storing the new recovery codes it shows.
A passkey that checks it is you, by fingerprint, face or PIN, also signs you in without the app's code.
If you have lost the app and every recovery code and have no such passkey, the sign-in page cannot let you in. Its code step offers What to do, which opens this section, and Contact us, which opens the contact form. Name the email address of your Costfluent account there; the reply goes to the address you enter in the form.
Connected accounts
Connected accounts lists the GitHub, Google or Microsoft accounts you can sign in with. To connect one, sign out, then sign in with GitHub, Google or Microsoft using the email address of your Costfluent account: a provider account that has verified that address connects to yours. Another address opens a separate Costfluent account. The card says so, with your address and the providers this deployment offers.
Disconnect removes a connected account. If it is the only way you can sign in, Disconnect is unavailable until you add a passkey or set a password, and the row says so, with links to both cards; see Your account for the password.
Connected apps
An app you sign in to with your Costfluent account, such as the costfluent command, reads one organization for you, as Sign in from an app describes. Open Settings, then Connected apps, to see the apps you connected to the organization. Revoke ends one at once: its next call is refused, and it asks you to sign in again. Seeing and revoking the connected apps of every member needs the Owner organization role; every other member sees and revokes their own.
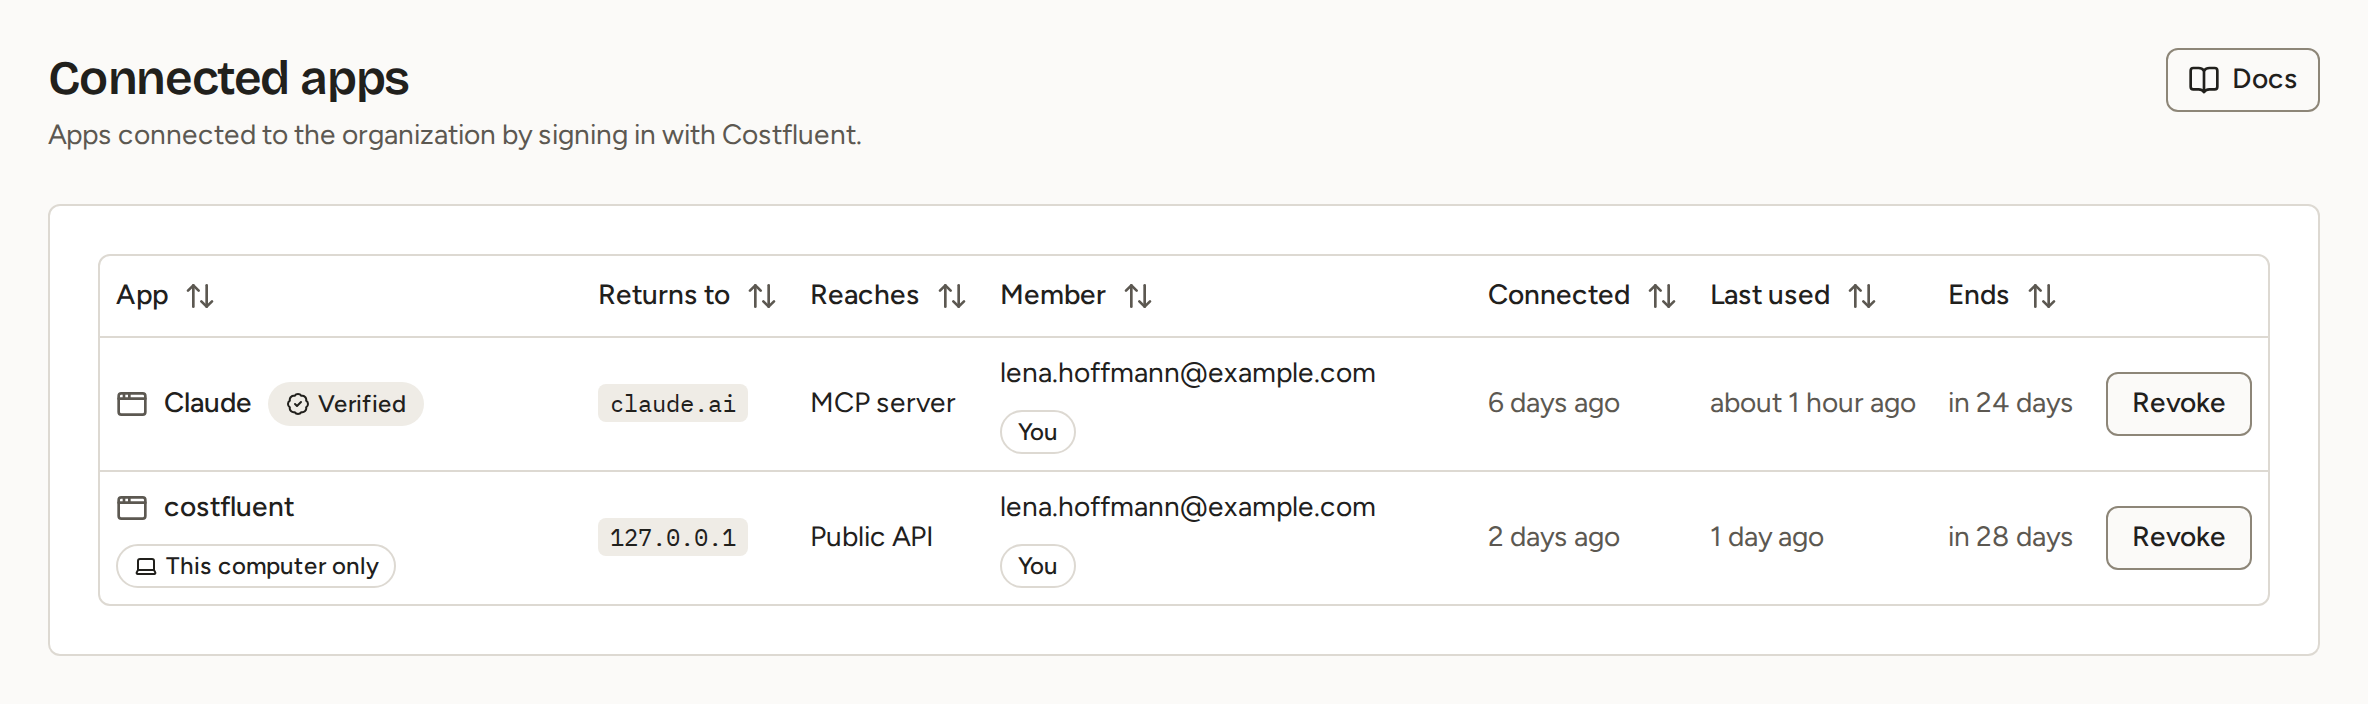
An app's connection ends 30 days after the sign-in that approved it, or 24 hours after when that sign-in was through single sign-on, however often the app is used; then the app asks you to sign in again. It ends sooner when the session you approved it from ends: when you select Sign out for that session under Sessions or sign out in that browser, when you select Sign out everywhere else from another session, when your organization turns on single sign-on enforcement and ends that session, and when that session next tries to renew and is refused after an organization you belong to starts requiring two-factor authentication or single sign-on of you. It also ends when every session of yours is ended, and when you change your password, whichever session you change it from: when your password is changed or reset, when your email address changes, when an Owner selects Sign out for you under Users and when your account is deleted. Removing you from the organization ends your connected apps there. Until then the app never reads more than you may: a lower role or fewer workspaces apply to its next call, and while you are suspended its calls are refused.
Connect single sign-on
Open Settings, then Single sign-on. Costfluent connects to any OpenID Connect provider: Microsoft Entra ID, Google Workspace, Okta, Keycloak, JumpCloud, Authentik and others. An organization can hold one connection per identity provider, and each connection can serve several email domains; a domain belongs to one connection.
- Register Costfluent at your identity provider first, as Add a connection says at its top: create an OpenID Connect web application there, which issues the Client ID and Client secret you enter below, and where your provider asks how Costfluent authenticates, choose a client secret sent in the body of the token request (
client_secret_post). The redirect URI comes in step 8, once the connection is saved. The card links the guide for each provider: Microsoft Entra ID, Google Workspace, Okta, Keycloak, JumpCloud and Authentik. - Under Add a connection, enter the Email domain whose people should sign in through your provider. You add further domains to the connection once it is saved.
- From your provider, enter the Discovery URL (the OpenID Connect discovery document, usually ending in
/.well-known/openid-configuration), the Client ID and the Client secret. The secret is stored encrypted in the database and never shown again. To rotate it later, type the new one under Client secret on the connection and select Replace secret: the connection stays enabled and enforced. Saving a domain the connection already serves in this form again sets the connection up again, which switches it off until you enable it again; its domains stay verified. - Under Groups claim, enter the claim your provider puts group names in, or leave it empty for
groups. - Choose the Default role for people Costfluent creates: Viewer or Editor. Owner cannot be granted this way.
- Leave Create accounts automatically on if a person signing in for the first time should get an account at the default role.
- Select Save connection.
- Copy the connection's Redirect URI,
https://app.costfluent.com/api/auth/sso/callback/followed by the connection's own ID, and register it at your provider exactly as shown, without a wildcard. Your provider refuses every sign-in through the connection until it holds that exact address. Removehttps://app.costfluent.com/api/auth/sso/callbackif your provider still holds it from an earlier setup: Costfluent no longer uses it. Saving the connection again keeps its Redirect URI; removing the connection and adding it again gives it a new one, which you register again.
Costfluent stores the issuer the discovery document names when you save. Every sign-in afterwards must come from exactly that issuer, so a discovery URL that starts naming another issuer stops signing anyone in until you save the connection again. Saving a connection with another issuer forgets which provider account each member signed in with, because a new provider's accounts are new people to Costfluent: each member is matched again by their address at a verified domain at their next sign-in, and is emailed when that happens.
Verify the domains
Each domain of a connection is proved by its own TXT record, under Domains on the connection.
- Select Show the TXT record next to the domain and publish it in that domain's DNS.
- Select Verify domain. If the record is not found yet, wait for DNS to propagate and try again.
A record's value verifies for seven days. Until the domain is verified or those days run out, the record stays under the domain with the date it stops verifying, so coming back later shows the same one. New TXT record replaces it, and the value already published then no longer verifies.
To serve another domain, enter it under Add a domain, select Add domain, and verify it the same way. Until it is verified it signs nobody in. A connection keeps at least one domain; removing the last verified one switches the connection off.
Keep the TXT record published for as long as the domain signs people in. Costfluent looks it up every day:
- When the record is missing, the domain's badge reads “Proof failing, lapses” and the date it lapses, and each Owner of the organization is emailed. Publish the record again, or select Show the TXT record, publish the new value and select Verify domain, before that date. The badge reads the same while lookups fail and for a domain that has to be verified once more (below), which only a new value and Verify domain prove.
- A domain whose record is still missing on the first daily check 7 days after it was first found missing lapses, and so does one whose lookups have failed for 30 days. The Owners are emailed again when it lapses.
- A lapsed domain signs nobody in. If it was the connection's last verified domain, Enabled and Require single sign-on are switched off, as removing it does, and members sign in with a password or a sign-in code. Verifying the domain again switches neither back on: turn on Enabled, then Require single sign-on, again.
- A domain verified before Costfluent kept its record has to be verified once more: its Owners are emailed the date, 30 days after the first daily check.
A domain another organization has verified can still be added. Verifying it succeeds only once that organization's record is gone: a record that holds only your value counts as missing for the other organization, which starts its 7 days and emails its Owners, and once those days have passed, verifying again lapses the other organization's domain and verifies yours. While the other organization's value is still published, verifying is refused with "The domain is already verified by another organization".
The verified domain is what Costfluent trusts: an address at one of the connection's verified domains signs in whatever the provider says about verifying the address, which is how Microsoft Entra ID (it never says) and Keycloak (it says no for imported users) sign in. An address outside every verified domain of the connection is refused. When a first sign-in links a Costfluent account that already existed, Costfluent emails that address to say so.
Enable and enforce
The connection's switches unlock in order: a domain is verified first, then Enabled, then Require single sign-on.
- Enabled allows sign-in through your provider for people at the connection's verified domains.
- Require single sign-on makes everyone sign in through it, and ends every other session except those of break-glass Owners: Owners with a password and a second factor who are exempt from single sign-on. Costfluent refuses to turn it on without at least one break-glass Owner, and says so.
- Break-glass owners, shown once the domain is verified, lists the organization's Owners with a switch each. An Owner can be marked only once they have a password and a second factor or passkey; until then the row reads "Needs a password and a second factor or passkey". While any connection has Require single sign-on on, the last break-glass Owner cannot be unmarked under any connection and cannot be suspended, and cannot remove the authenticator app or a passkey when neither would be left.
While the connection is Enabled, the sign-in page sends a person at one of its domains to the provider as soon as they enter their email address. The sign-up page does the same only while Create accounts automatically is on or single sign-on is required; otherwise a person without an account signs up with a password, because the provider would only tell them to ask for an invitation. Once single sign-on is required, a sign-up with a password at those domains also sends the person to the provider instead of opening an account, and an invitation to such an address is accepted by signing in there.
Remove connection sends people at its domains back to signing in with a password.
Map groups to teams
Under Group to team mapping:
- Enter the Identity provider group as your provider sends it.
- Choose the Team.
- Select Add mapping.
Each sign-in through the connection puts the person in the teams their groups map to, and takes them out of a mapped team once the group is gone. Their role in a mapped team follows their organization role, including when you change it later, and cannot be set by hand, in the product or through the API. A team someone was added to by hand is never changed.
Your provider must send the groups in the claim the connection reads (groups unless you set another Groups claim), in the ID token or from userinfo, and names must match exactly. Keycloak sends paths such as /engineering, and Google Workspace sends no groups at all, so map those people by hand. Microsoft Entra ID sends group object IDs, and leaves the claim out for a person in more than 200 groups. Costfluent then adds no team for that sign-in and removes only a team whose mapping you deleted or changed. To keep the claim small, assign the groups you map to the application in Entra ID and limit the groups claim to "Groups assigned to the application"; a person in more than 200 of those groups still gets no claim.
Provision with SCIM
With SCIM provisioning, your identity provider creates, suspends and removes the people of a connection's verified domains and places them in teams, without anyone inviting them. Costfluent speaks SCIM 2.0 to Okta and Microsoft Entra ID. Under Provisioning (SCIM) on the connection:
- Verify a domain of the connection, then select Generate token.
- Copy the SCIM base URL and the token under Your SCIM token, then select Done. The token is shown only this once.
- In Okta, turn on SCIM provisioning for the application, enter the base URL as its SCIM connector base URL,
userNameas the unique identifier for users, and the token as an HTTP header bearer token, then allow pushing new users, profile updates and groups. In Microsoft Entra ID, set the enterprise application's provisioning mode to automatic, enter the base URL as the tenant URL and the token as the secret token, and test the connection. - Assign the people and groups to the application in your provider.
The section then shows Connected, when, and when the provider Last used the token. What provisioning changes:
- A person whose address is in a verified domain of the connection becomes a member with the connection's Default role, in the Everyone team, and their address is confirmed at their first sign-in through single sign-on. An address outside the verified domains is refused, and so is a person who is already a member; an invited or removed person is made a member.
- Deactivating or unassigning a person in the provider suspends them, and activating them again restores them, unless they were suspended in Costfluent with Suspend: they then stay suspended until someone chooses Reactivate; for a person invited but not yet joined, it ends their invitation, so its link no longer works, and activating them makes them a member; deleting them removes them from the organization and every team. The organization's last active Owner is never suspended or removed.
- A group the provider pushes becomes a team: the team the connection already maps that group to under Group to team mapping, else the team of the same name, else a new team. The people it adds follow their organization role there, and someone added to the team by hand is never removed. Deleting the group in the provider takes its people out of the team, and the team stays.
- While provisioning is connected, signing in no longer changes teams from the groups claim.
- Provisioning never changes a person's address, which they change in Costfluent themselves (a new username from your provider is ignored, and the rest of the change, a deactivation included, still applies), never makes anyone an Owner or Integration owner, and renames a person only while they are an active member of no other organization. Each change is in the audit log as an event starting with
scim., made by the SCIM token.
A group must map to one team, and a team must take one group. Your provider is refused a group the connection maps to several teams, and a team several groups map to, until you keep one mapping. The Everyone team cannot be provisioned.
Provisioning, your provider's first sync included, runs on a request budget of its own, apart from the organization's API tokens, so neither slows the other. Past that budget, Costfluent answers 429 with Retry-After and your provider tries again later. Public API rate limits says how the budget works.
Revoke token stops provisioning; the members and team memberships it created stay, and signing in applies Group to team mapping again. Remove connection revokes the token too. The token belongs to the connection, not to the Owner who generated it, so it keeps working after they leave the organization; if they kept a copy, revoke it and generate another.
Require two-factor authentication
An Owner can require a second factor of every member: open Settings, then Organization, and under Two-factor authentication turn on Require two-factor authentication, then confirm with Require two-factor authentication. Turning it off needs no confirmation. Every change is recorded in the audit log.
- A member without an authenticator app who signs in with a password, a connected account or an email confirmation link gets no session yet. After a password, they first enter the emailed code, which does not meet the requirement. They then see Set up two-factor authentication: they scan the QR code with their authenticator app, or add Costfluent with the secret key or Open in authenticator app, type its six-digit code, and then see ten recovery codes once, under Save your recovery codes. Continue signs them in.
- A single sign-on sign-in is exempt from the requirement of the organization whose identity provider it went through: that provider is the strong factor. When another organization you belong to requires two-factor authentication, the sign-in still asks for the app's code, or for the setup above, before you get in.
- A passkey sign-in is exempt when the device checked who you are, with a PIN, a fingerprint or your face: the passkey is then the strong factor. A security key that asks only for a touch counts like a password, so its sign-in asks for the app's code, or for the setup above. If you have an authenticator app, such a sign-in asks for its code whether or not anything requires it.
- A member who already has an authenticator app signs in as before, with its code after the password.
- A member who still needs to set one up cannot renew a session, so sessions they opened before the requirement end within 15 minutes, and the next sign-in asks them to set it up.
- A member who has an authenticator app but whose session began without its code, with a touch-only security key, an email confirmation link or through single sign-on at another organization's identity provider, cannot renew that session either; the next sign-in asks for the app's code.
- A person who belongs to several organizations sets one up if any of them requires it.
- API tokens keep working: the requirement governs signing in, not the Public API. A token created before the requirement was turned on, also by a member who has no second factor yet, works until it expires or an Owner revokes it. Connected apps, by contrast, end when the session they were approved from next tries to renew and is refused under the requirement; turning the requirement on ends none by itself, and the member connects them again after the next sign-in. See Public API authentication.
- The requirement binds a partner's staff who manage the organization too, in the session they use, as it binds members. To enter it they need a session that began with their authenticator app's code, a passkey sign-in that checked who they are, or a single sign-on session while an authenticator app is set up on their account. Without an authenticator app the organization refuses them with "This organization requires two-factor authentication. Set up an authenticator app for your account to enter it." and the link Set up an authenticator app, which opens the section above on Security. With one, but in a session that began without its code, with a password and the emailed code, a connected account, a touch-only security key or an email confirmation link, it refuses them with "For your security, sign in again before making this change."; signing in again with the app's code lets them in. Their own organization and the partner's other managed organizations stay open to them.